A New Standard of Security Powered by AI
Clumit Security combines unsupervised learning-based AI clustering with security-optimized LLM analysis to detect new and variant threats in real time and automatically analyze detected events to suggest response measures. In preparation for Mythos-style vulnerability discovery AI and offensive AI agents abusing normal privileges and normal traffic, Clumit Security monitors inbound, outbound, and lateral traffic, detects anomalies through AI clustering, and uses LLMs to provide natural-language reports on threat essence, impact scope, and response priorities.
By integrating detection, analysis, and report generation into a single process, security teams can move beyond repetitive detection validation and report writing, and focus on faster, more precise response and strategy development.
Main Functions
Comprehensive Threat Detection Across the Cyber Kill Chain
Analyze inbound, outbound, and lateral traffic
Detect threat elements active in the early and middle stages of attacks
Early identification of novel and variant behavior, normal privilege abuse, lateral movement, covert channels, and data exfiltration signals created by autonomous attack tools
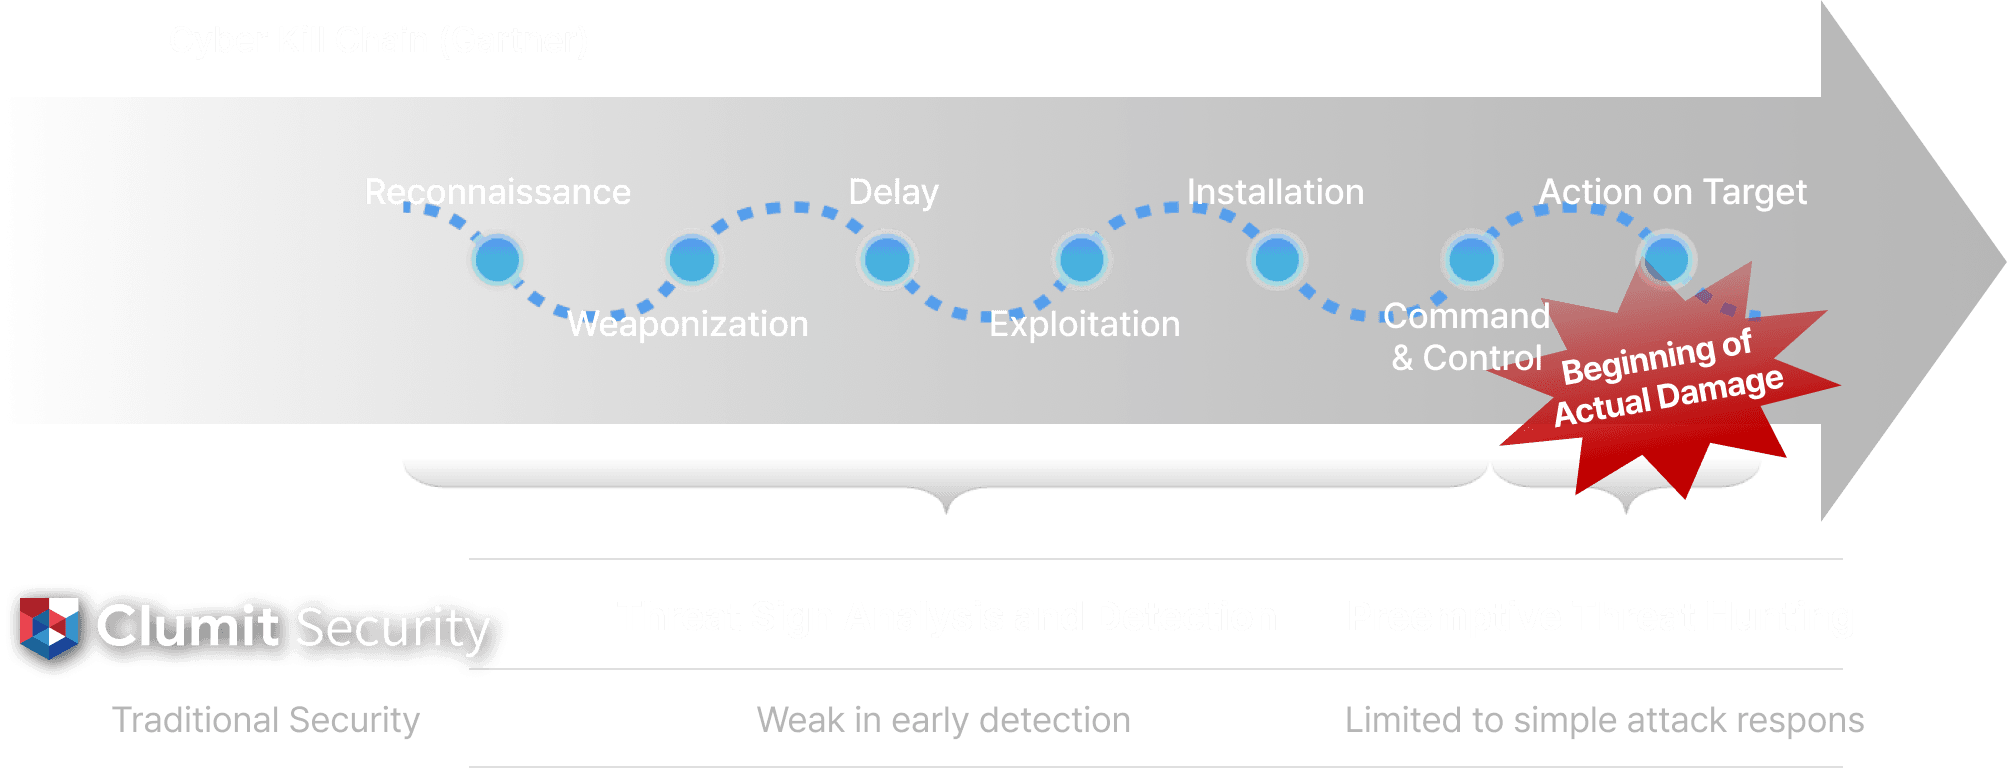
AI Clustering and Automated Labeling for Emerging Threats
Identifies abnormal behavior in real time with AI clustering
Scores threats based on severity and confidence levels
Generates regular expressions from real-time threat data, compares with a knowledge database, and automatically labels them to classify new or emerging threats
Semi-Supervised Models for High-Risk Threat Detection
Specialized semi-supervised models to detect high-risk threats such as ransomware and covert communication channels
Dedicated detection for known but high-risk threats often missed by legacy solutions
Real-Time Report Generation with LLM Integration
Evaluate and analyze detection results from multiple angles through LLM integration
High-quality actionable reports containing event importance and response measures based on objective facts
Summarize what happened, why it matters, and what should be done in natural-language reports for anomalous behavior selected by AI clustering
Optimized for Diverse Network Environments
Deployable in air-gapped, large-scale, or small-scale networks, with flexible adaptation to different customer environments
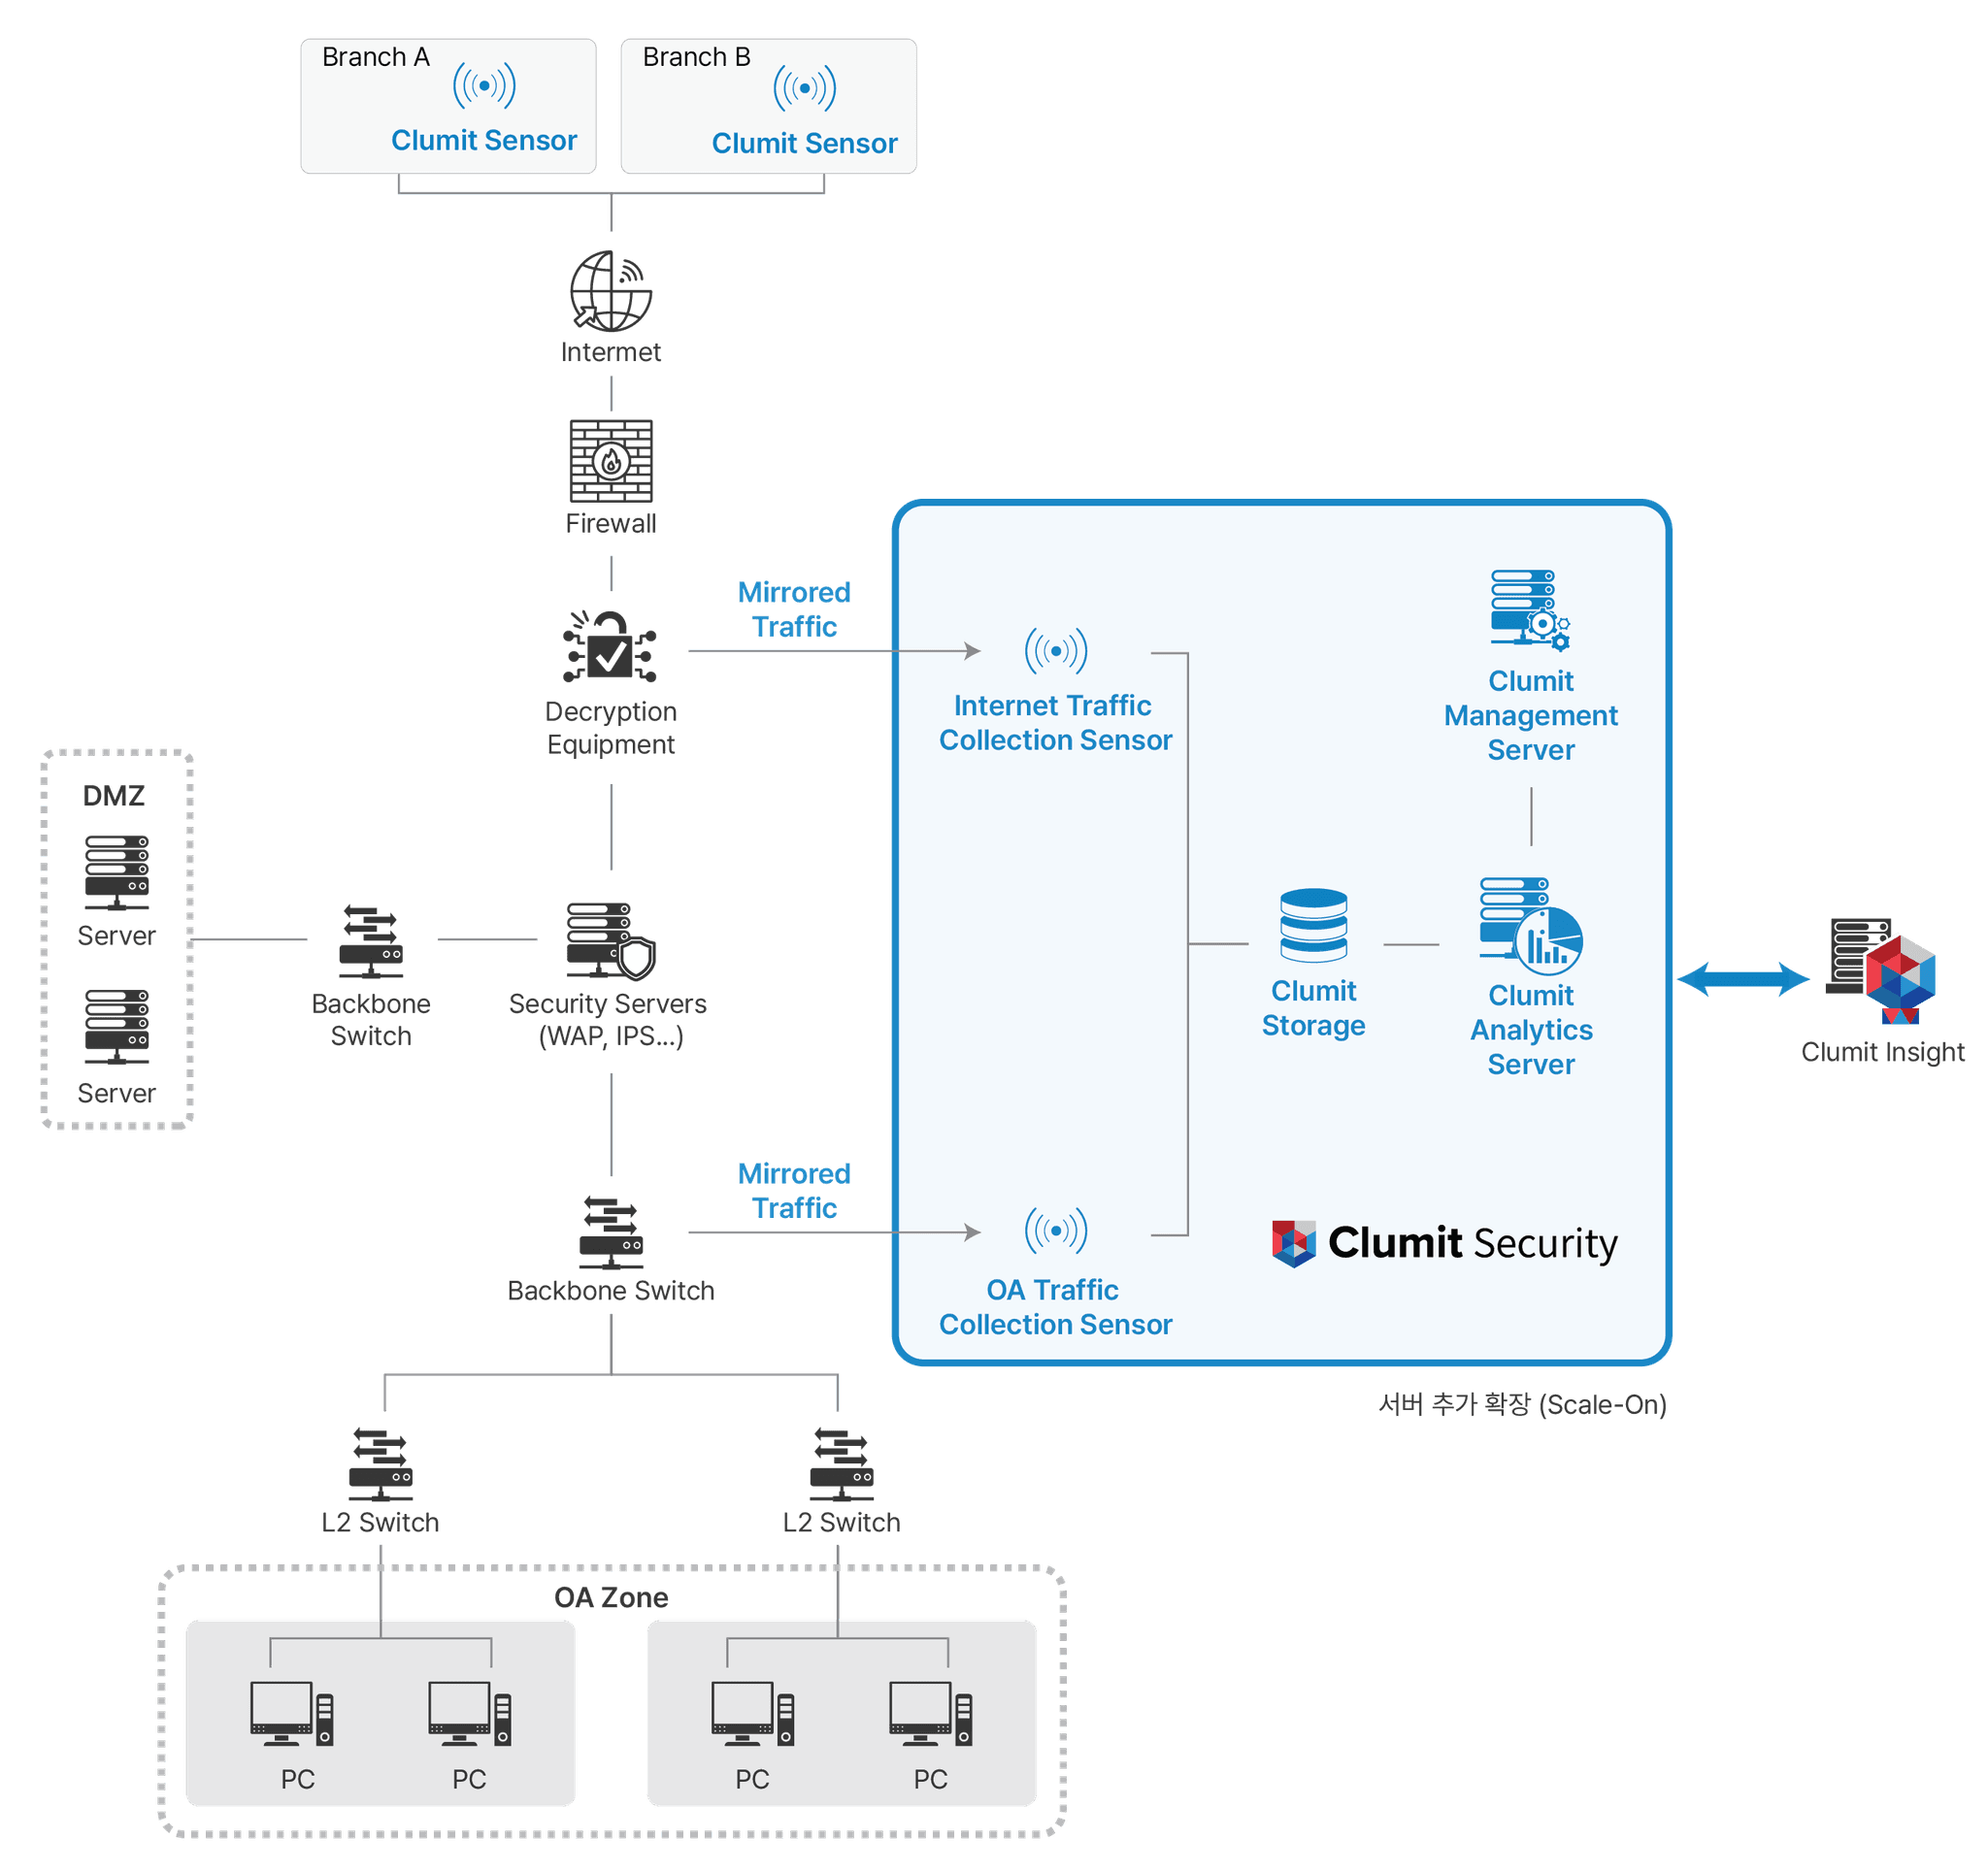
Closed Network (Air-Gapped)
Offline updates
Offline Threat Intelligence
Deployment of multiple sensors
Threat monitoring across all IT assets
Long-term storage of raw data
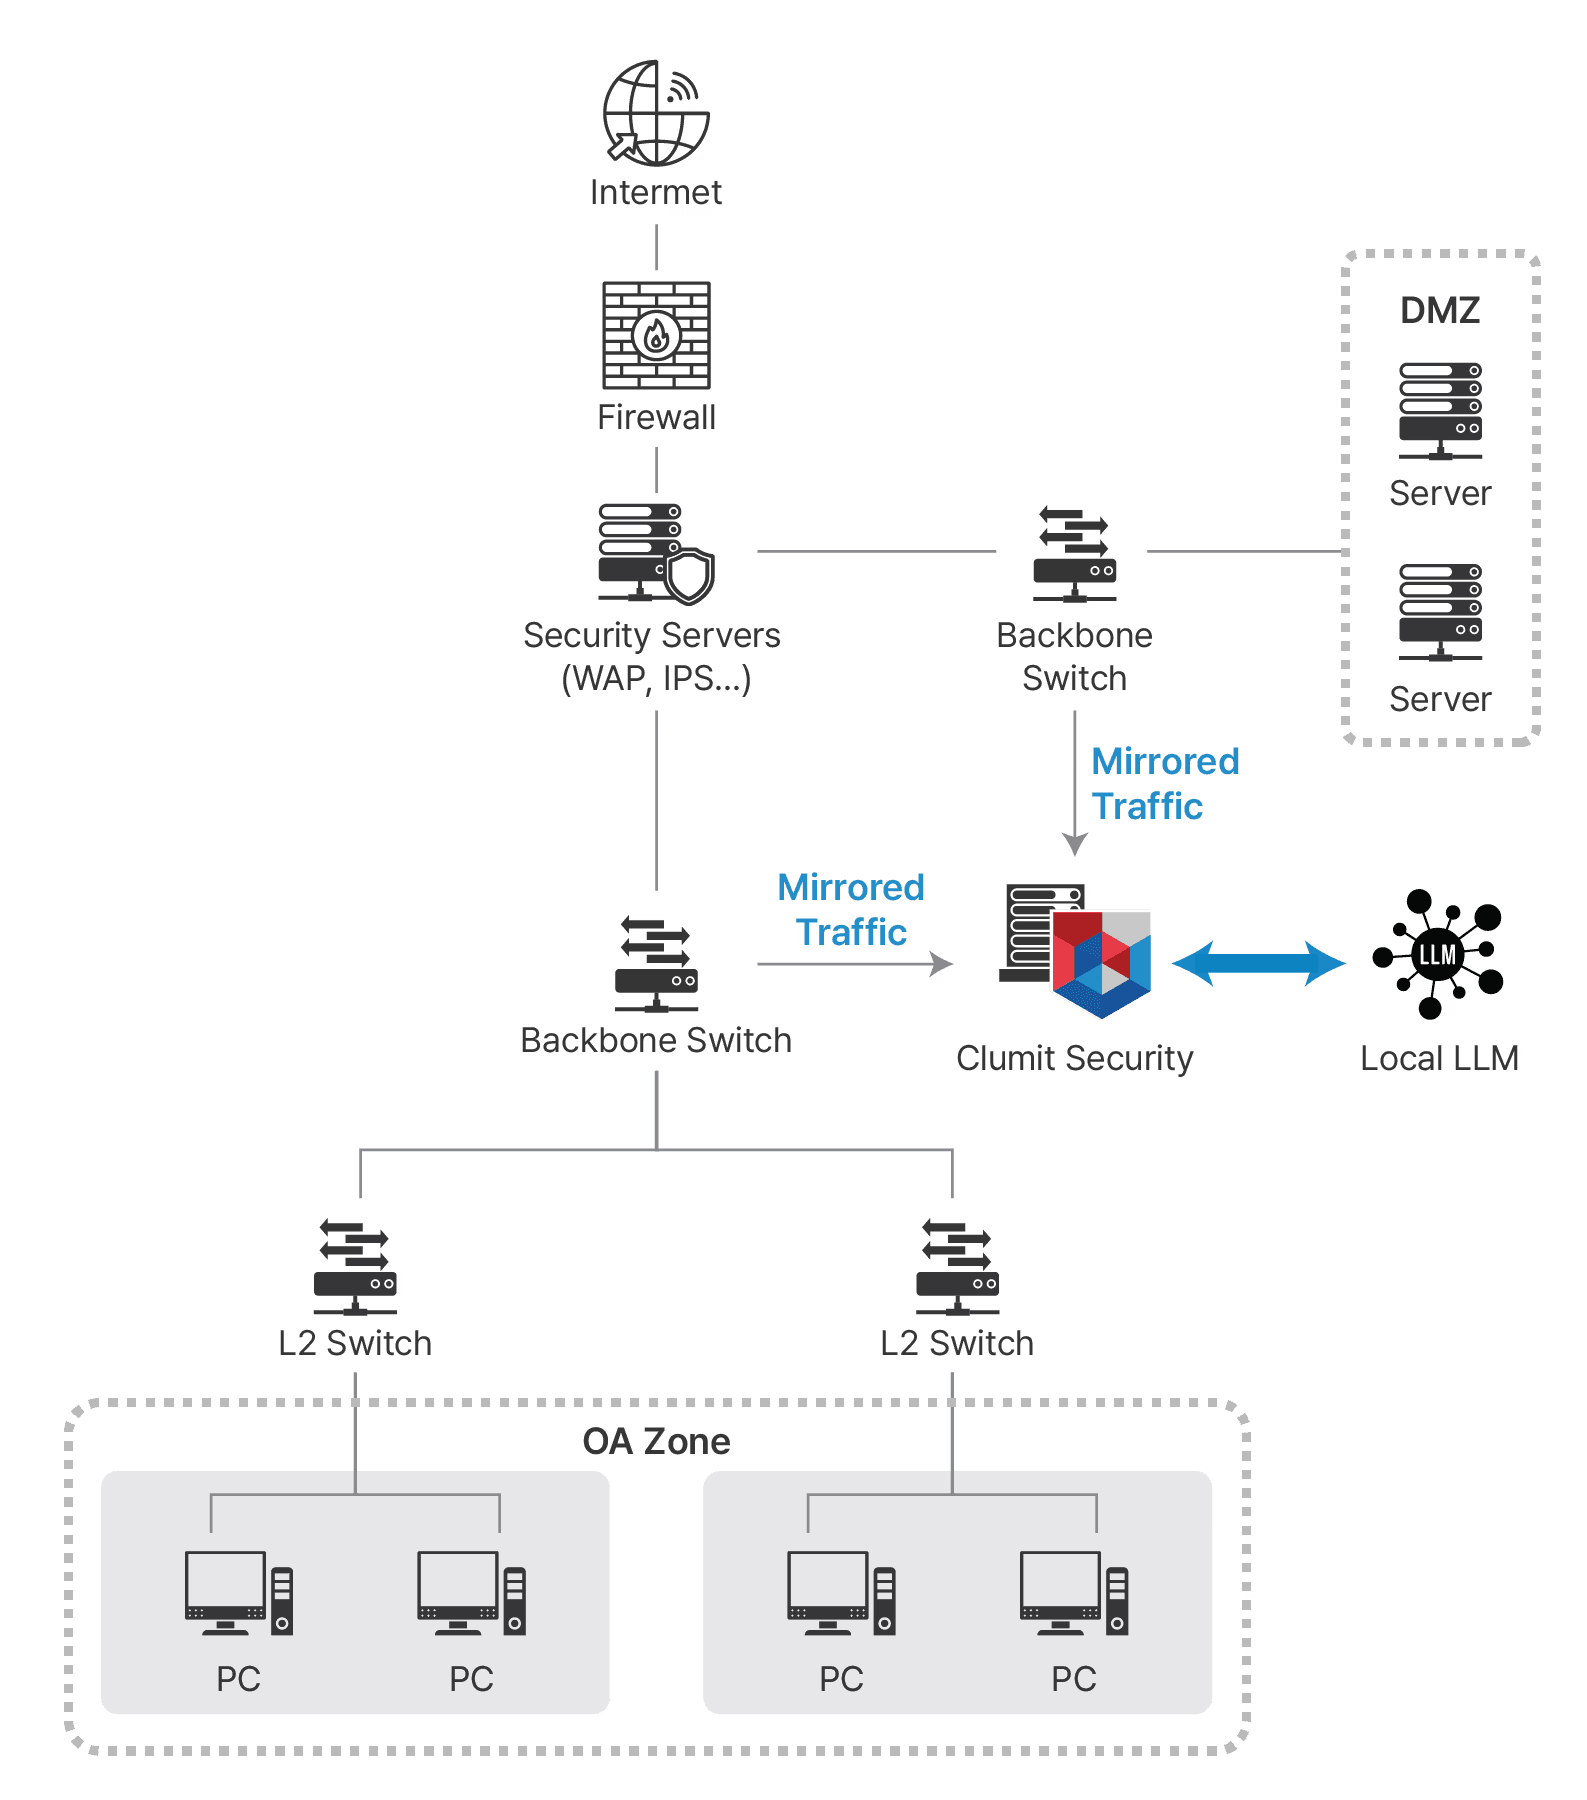
Small-Scale Network
Online automatic updates
Threat Intelligence integration
Monitoring of inbound/outbound internet threats
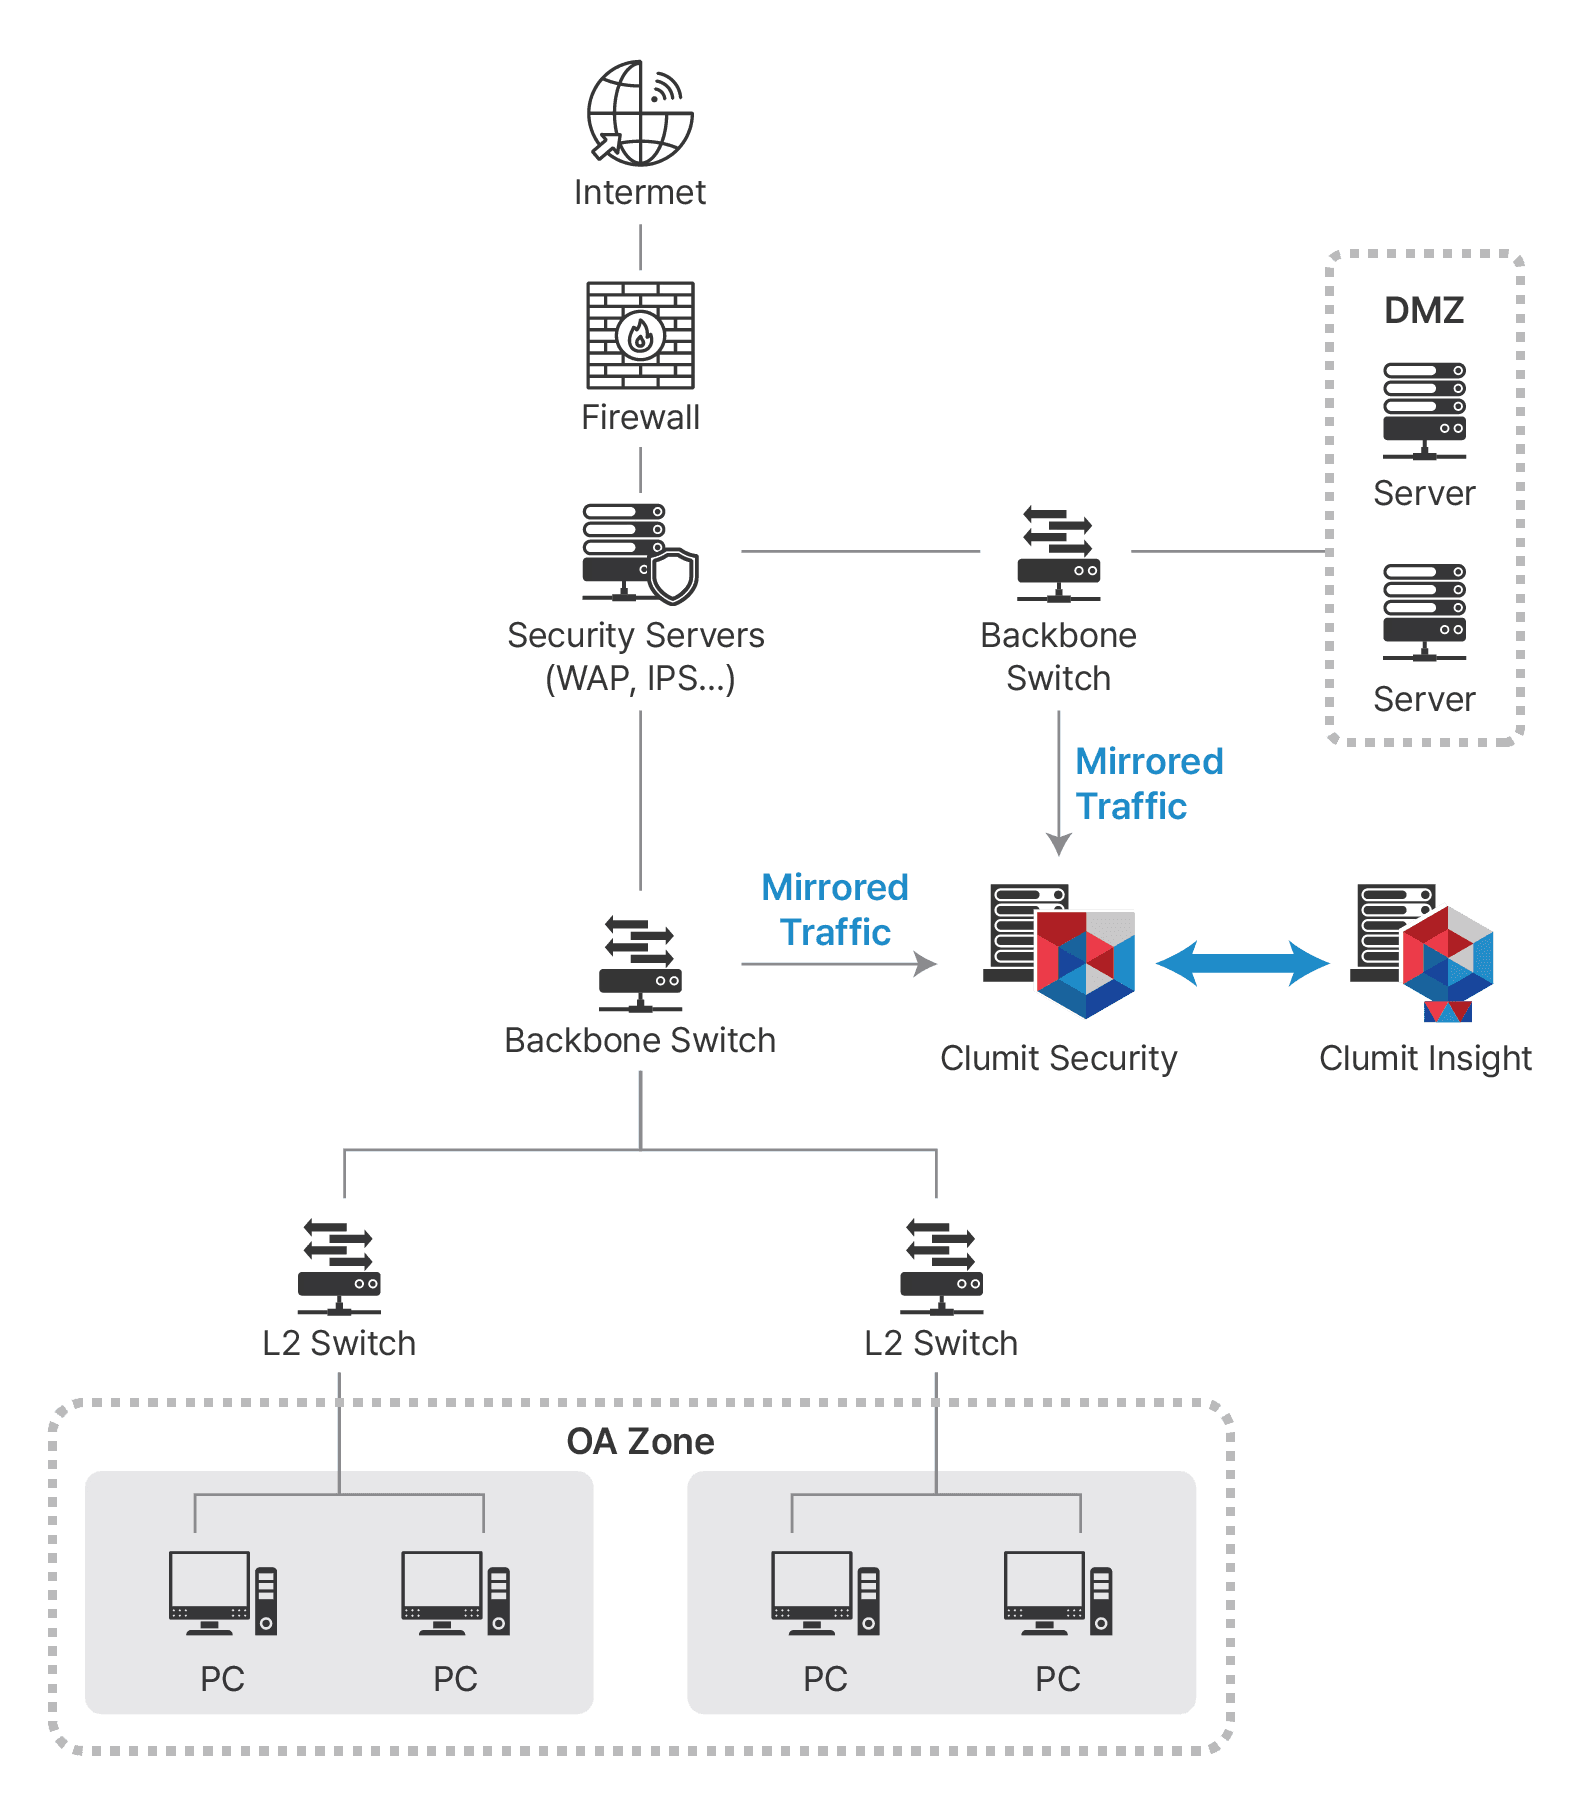
Large-Scale Network
Online automatic updates
Threat Intelligence integration
Tenant-based management by affiliate/subsidiary
Monitoring of inbound/outbound internet threats
Monitoring of key assets such as servers
Short-term storage of raw data
Features
Real-Time Detection of New and Emerging Threats
Automatic detection of abnormal traffic using AI clustering
Continuous identification of new threats through real-time analysis and AI model updates
Automated threat analysis linked directly to the response process
Automated Labeling with Threat Intelligence Databas
Provides tailored detection techniques through semi-supervised learning
Leverages Cyber Kill Chain–based models for threat-type–specific detection
Automatically labels detected threats by referencing the threat knowledge database
Real-Time Network-Wide Threat Analysis
Integrated monitoring of inbound, outbound, and lateral traffic
Flexible solution optimized for diverse network environments
Full Compliance with Security Standards and Regulations
Meets policy standards including Zero Trust Architecture and N²SF (National Network Security Framework – South Korea’s national cybersecurity framework for government and critical infrastructure networks)
Provides detection and reporting fully aligned with global and national regulatory requirements and guidelines