
- Proprietary AI Clustering Engine
The ClumL AI Clustering Engine is a high-performance, unsupervised learning–based clustering engine, protected by a U.S. patent, and serves as the core intelligence of autonomous security, capable of capturing not only threat signals but also their progression and flow.
Developed jointly by ClumL’s research teams in the U.S. and Korea, this engine is built on ClumL’s accumulated proprietary technology and serves as a key competitive advantage in the global market.
Principle and Structure
The engine identifies multi-dimensional behavioral patterns in unstructured raw data in real time, autonomously grouping data by similarity and pattern without predefined rules.
This makes it capable of detecting previously unknown anomalies and irregular behaviors, with a special design focus on capturing the flow and context of network threats.
Through high-performance Incremental Clustering, which can immediately incorporate real-time data updates, the engine ensures greater analytical accuracy and rapid detection of the latest threats.
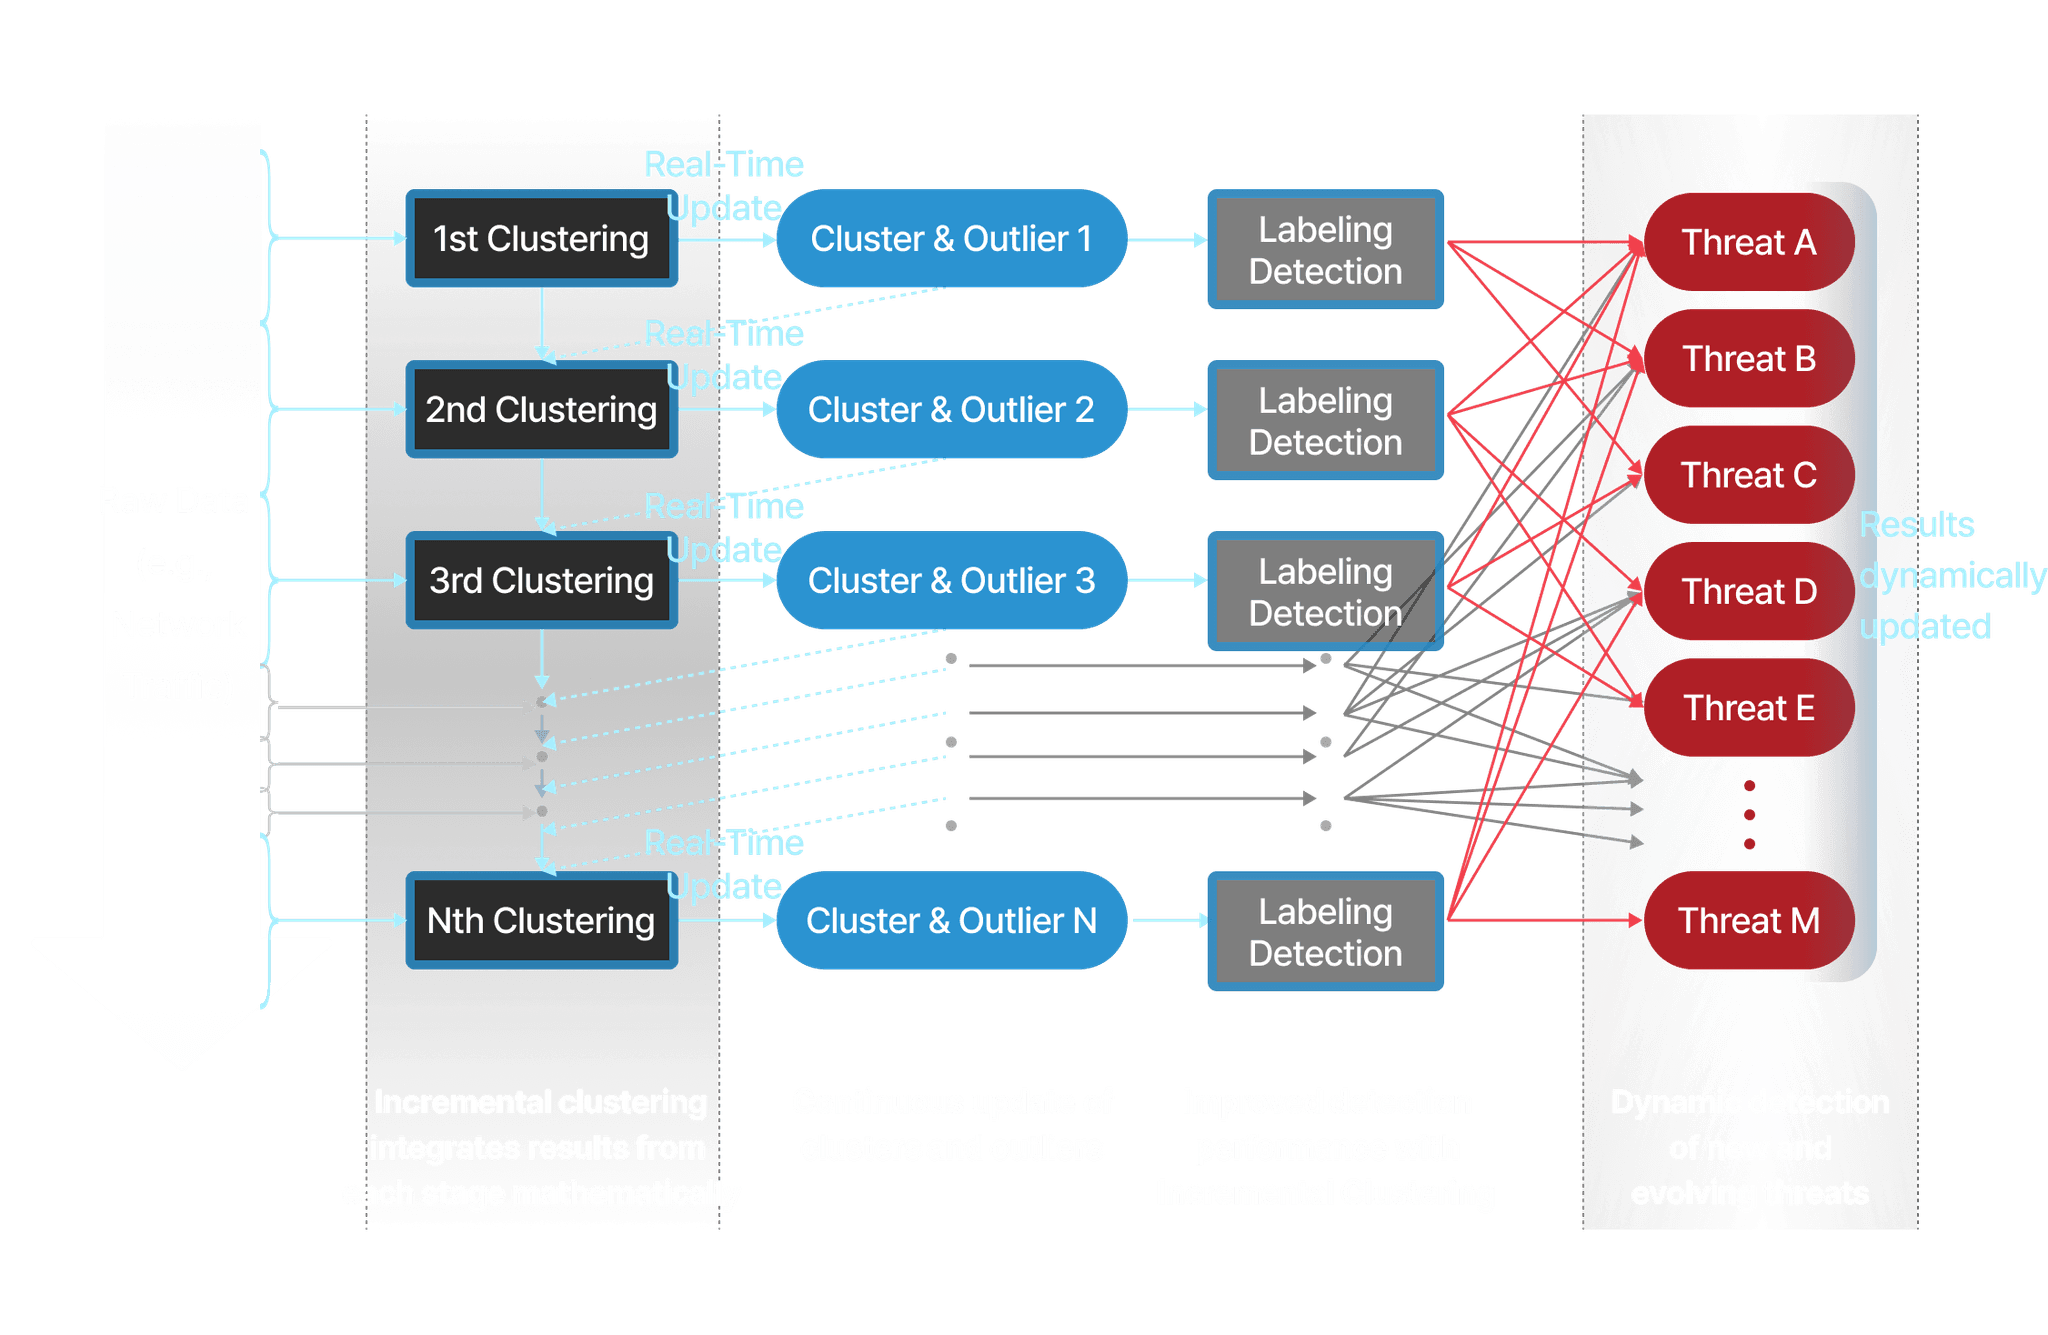
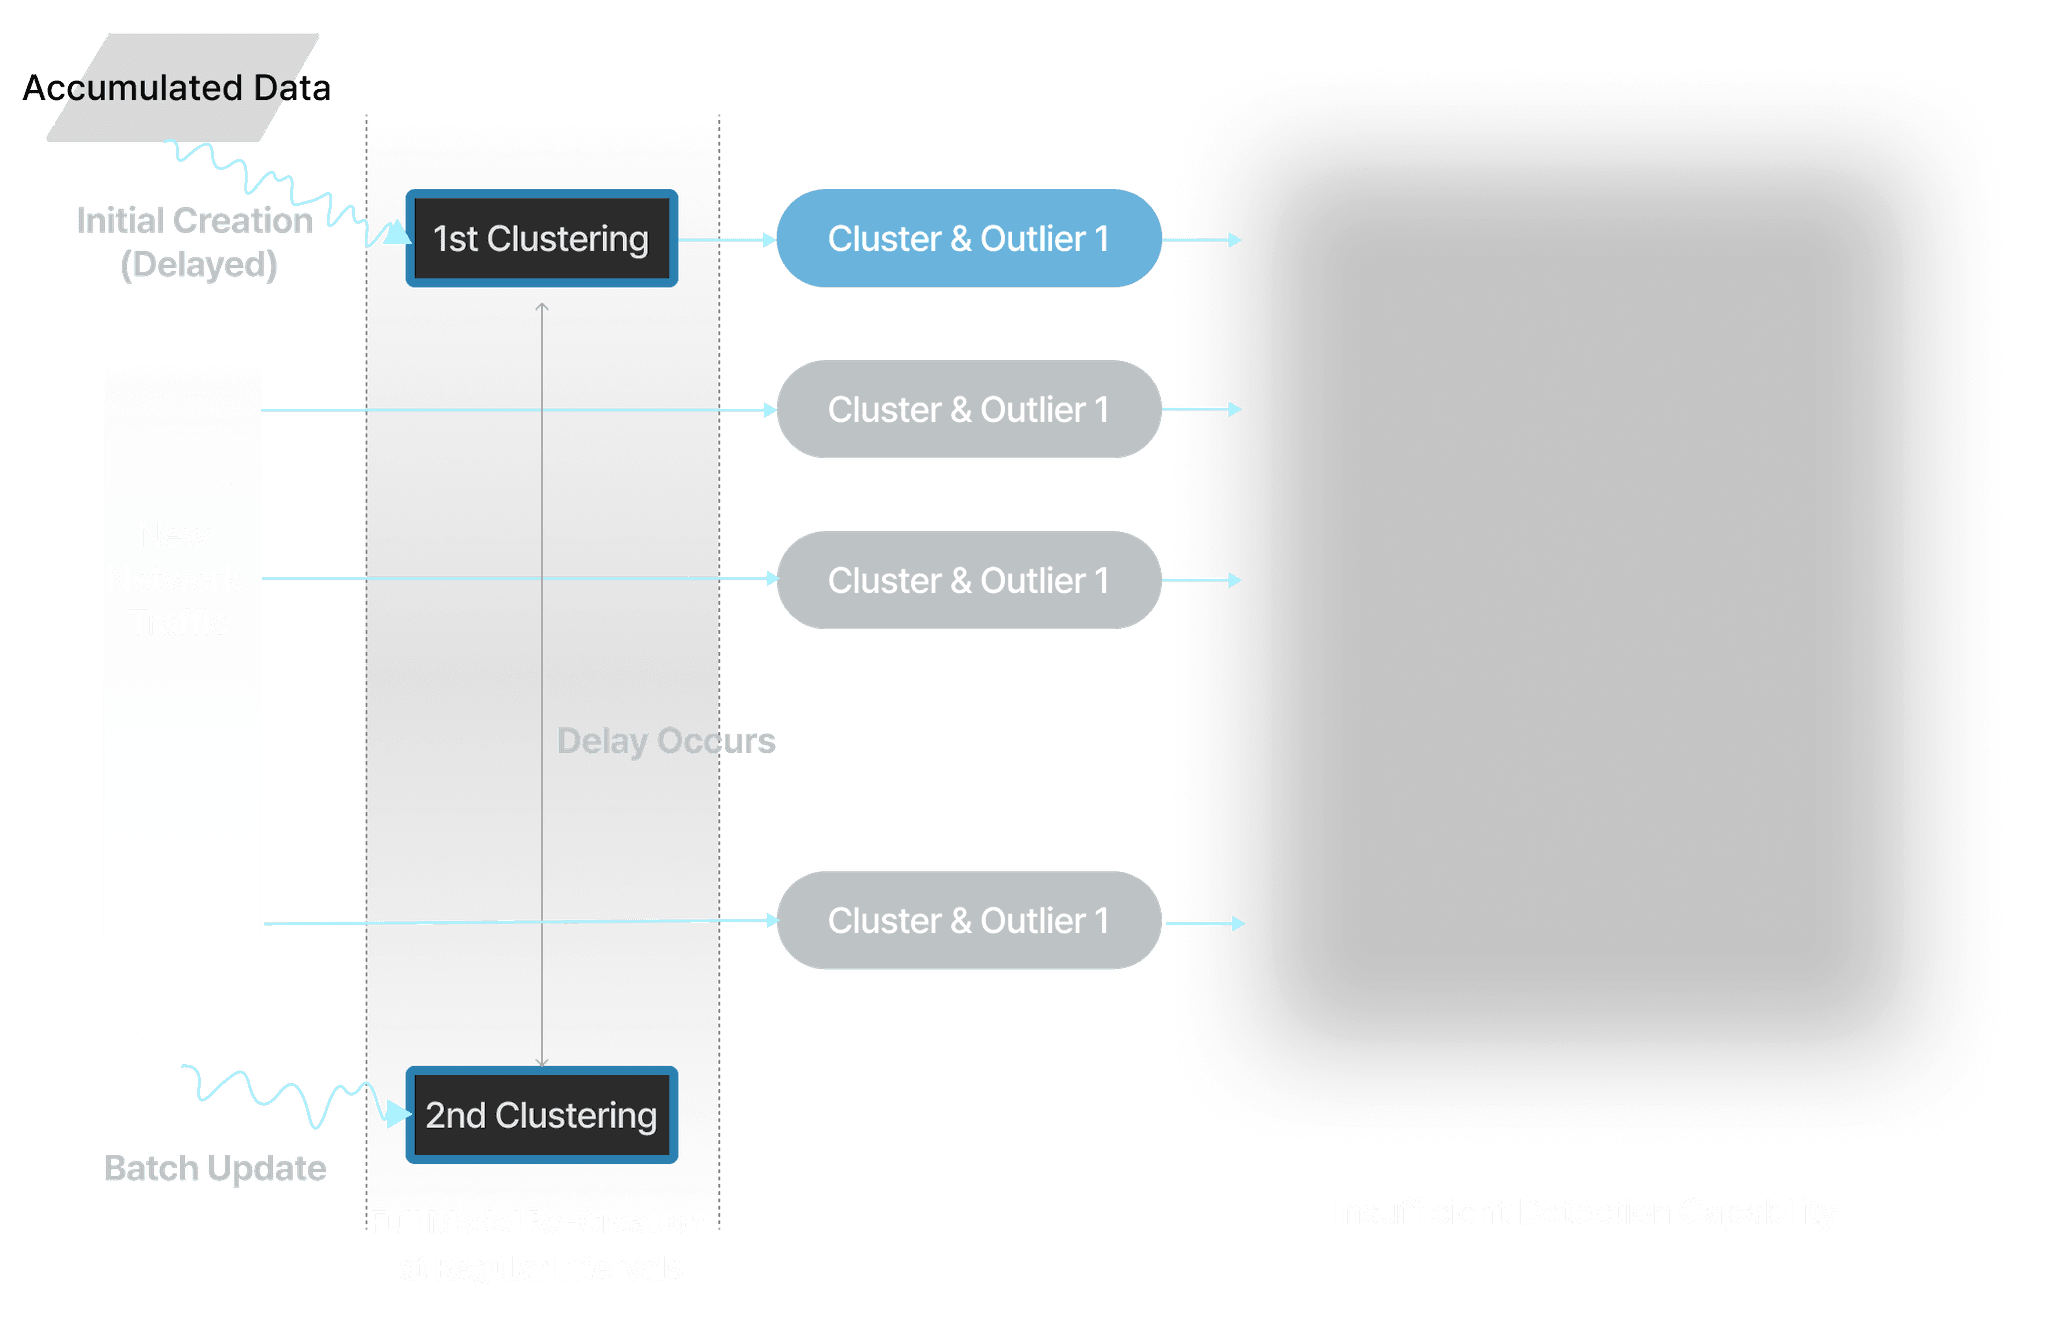
Differentiation: Clumit Incremental Clustering vs. Other AI Security Solutions
Real-Time Large-Scale Data Clustering
Analyzes both structured and unstructured data at backbone-level traffic scale
Captures the entire flow of malicious activities in real time
Abnormal Behavior Detection
Mirrors the entire network to detect abnormal communications such as suspicious domain connections or unusual data exfiltration at irregular times
Context-Aware Threat Detection
Clumit determines normal behavior by device and network, and detects threats within changing context by clustering time-series changes.
Offensive AI agents do not leave the same signature every time; they create abnormal sequences and context within normal privileges and normal traffic flows.
Clumit’s incremental clustering captures these anomalous signals within behavior patterns that change over time.
Expandable Raw Data Analysis Scope
Goes beyond real-time traffic to include diverse activity logs from endpoints and servers
Enables expanded clustering models tailored to specific detection objectives
Key Features
Real-Time Clustering of Large-Scale Data
Analyzes both structured and unstructured data at backbone-level traffic scale, capturing the entire flow of malicious activity in real time.
Abnormal Behavior Detection
Mirrors the entire network to identify suspicious communications such as abnormal domain access, as well as data exfiltration at unusual times.
Context-Aware Threat Detection
Autonomously learns normal behavior for each device and network, and clusters time-series changes to detect threats within evolving contexts—delivering the most advanced form of autonomous security.
Expandable Data Sources
Goes beyond real-time traffic, clustering diverse activity logs from endpoints and servers, enabling expanded modeling tailored to specific detection objectives.